Privacy and product analytics
Yekar.AI can collect product analytics - which pages of the app people visit - to understand how it is used and improve it. Two separate decisions govern it, and both must say yes before anything is collected.
Each person decides for themselves
After signing in, each person is asked once whether they want to share analytics data. Until they choose Share analytics, nothing is collected for them: the analytics client is not loaded and stores nothing in their browser.
- The answer belongs to the person and is saved to their account, so another device or workspace does not ask again. It is asked again after a year.
- It can be changed at any time under Settings → Account → Product analytics. Turning it off stops collection in that browser immediately and clears the analytics identifier stored there, and stops it on their other devices when they next load the account; it does not delete what was already collected.
- Nothing is collected during a support session, whatever the person chose.
What is collected is the page visited, identified by the person's account and workspace. Query strings and fragments are removed from every address, and no IP address is included in the events sent.
Session recording is the organization's decision
Settings → Privacy holds the organization's Session recording switch. It is off unless an organization Owner or Admin turns it on, and every change is written to the organization audit log with who made it.
When it is on, people in the organization who have also chosen Share analytics have their use of the app recorded as a replay, so usability problems can be found and fixed. Before anything leaves the browser:
- every input field and all on-screen text is masked;
- images, video, audio and embedded frames are blocked;
- no console output and no network request or response bodies are captured.
Turning the switch off stops recording as each person's app next refreshes, at the latest on their next page load; it does not delete recordings already made. If you turn it on, tell the people in your organization - they are the ones being recorded.
Sign out after inactivity
Settings → Privacy → Sign out after inactivity decides how long a browser signed in to your organization may sit unused before it has to sign in again. The default is three days. An organization Owner or Admin can make it shorter - down to 15 minutes - but not longer. A shorter time takes effect at once: a browser already idle for longer is signed out the next time it is used. Every change is written to the organization audit log. Each person can see their own signed-in browsers, and sign any of them out, under Settings → Account → Where you're signed in.
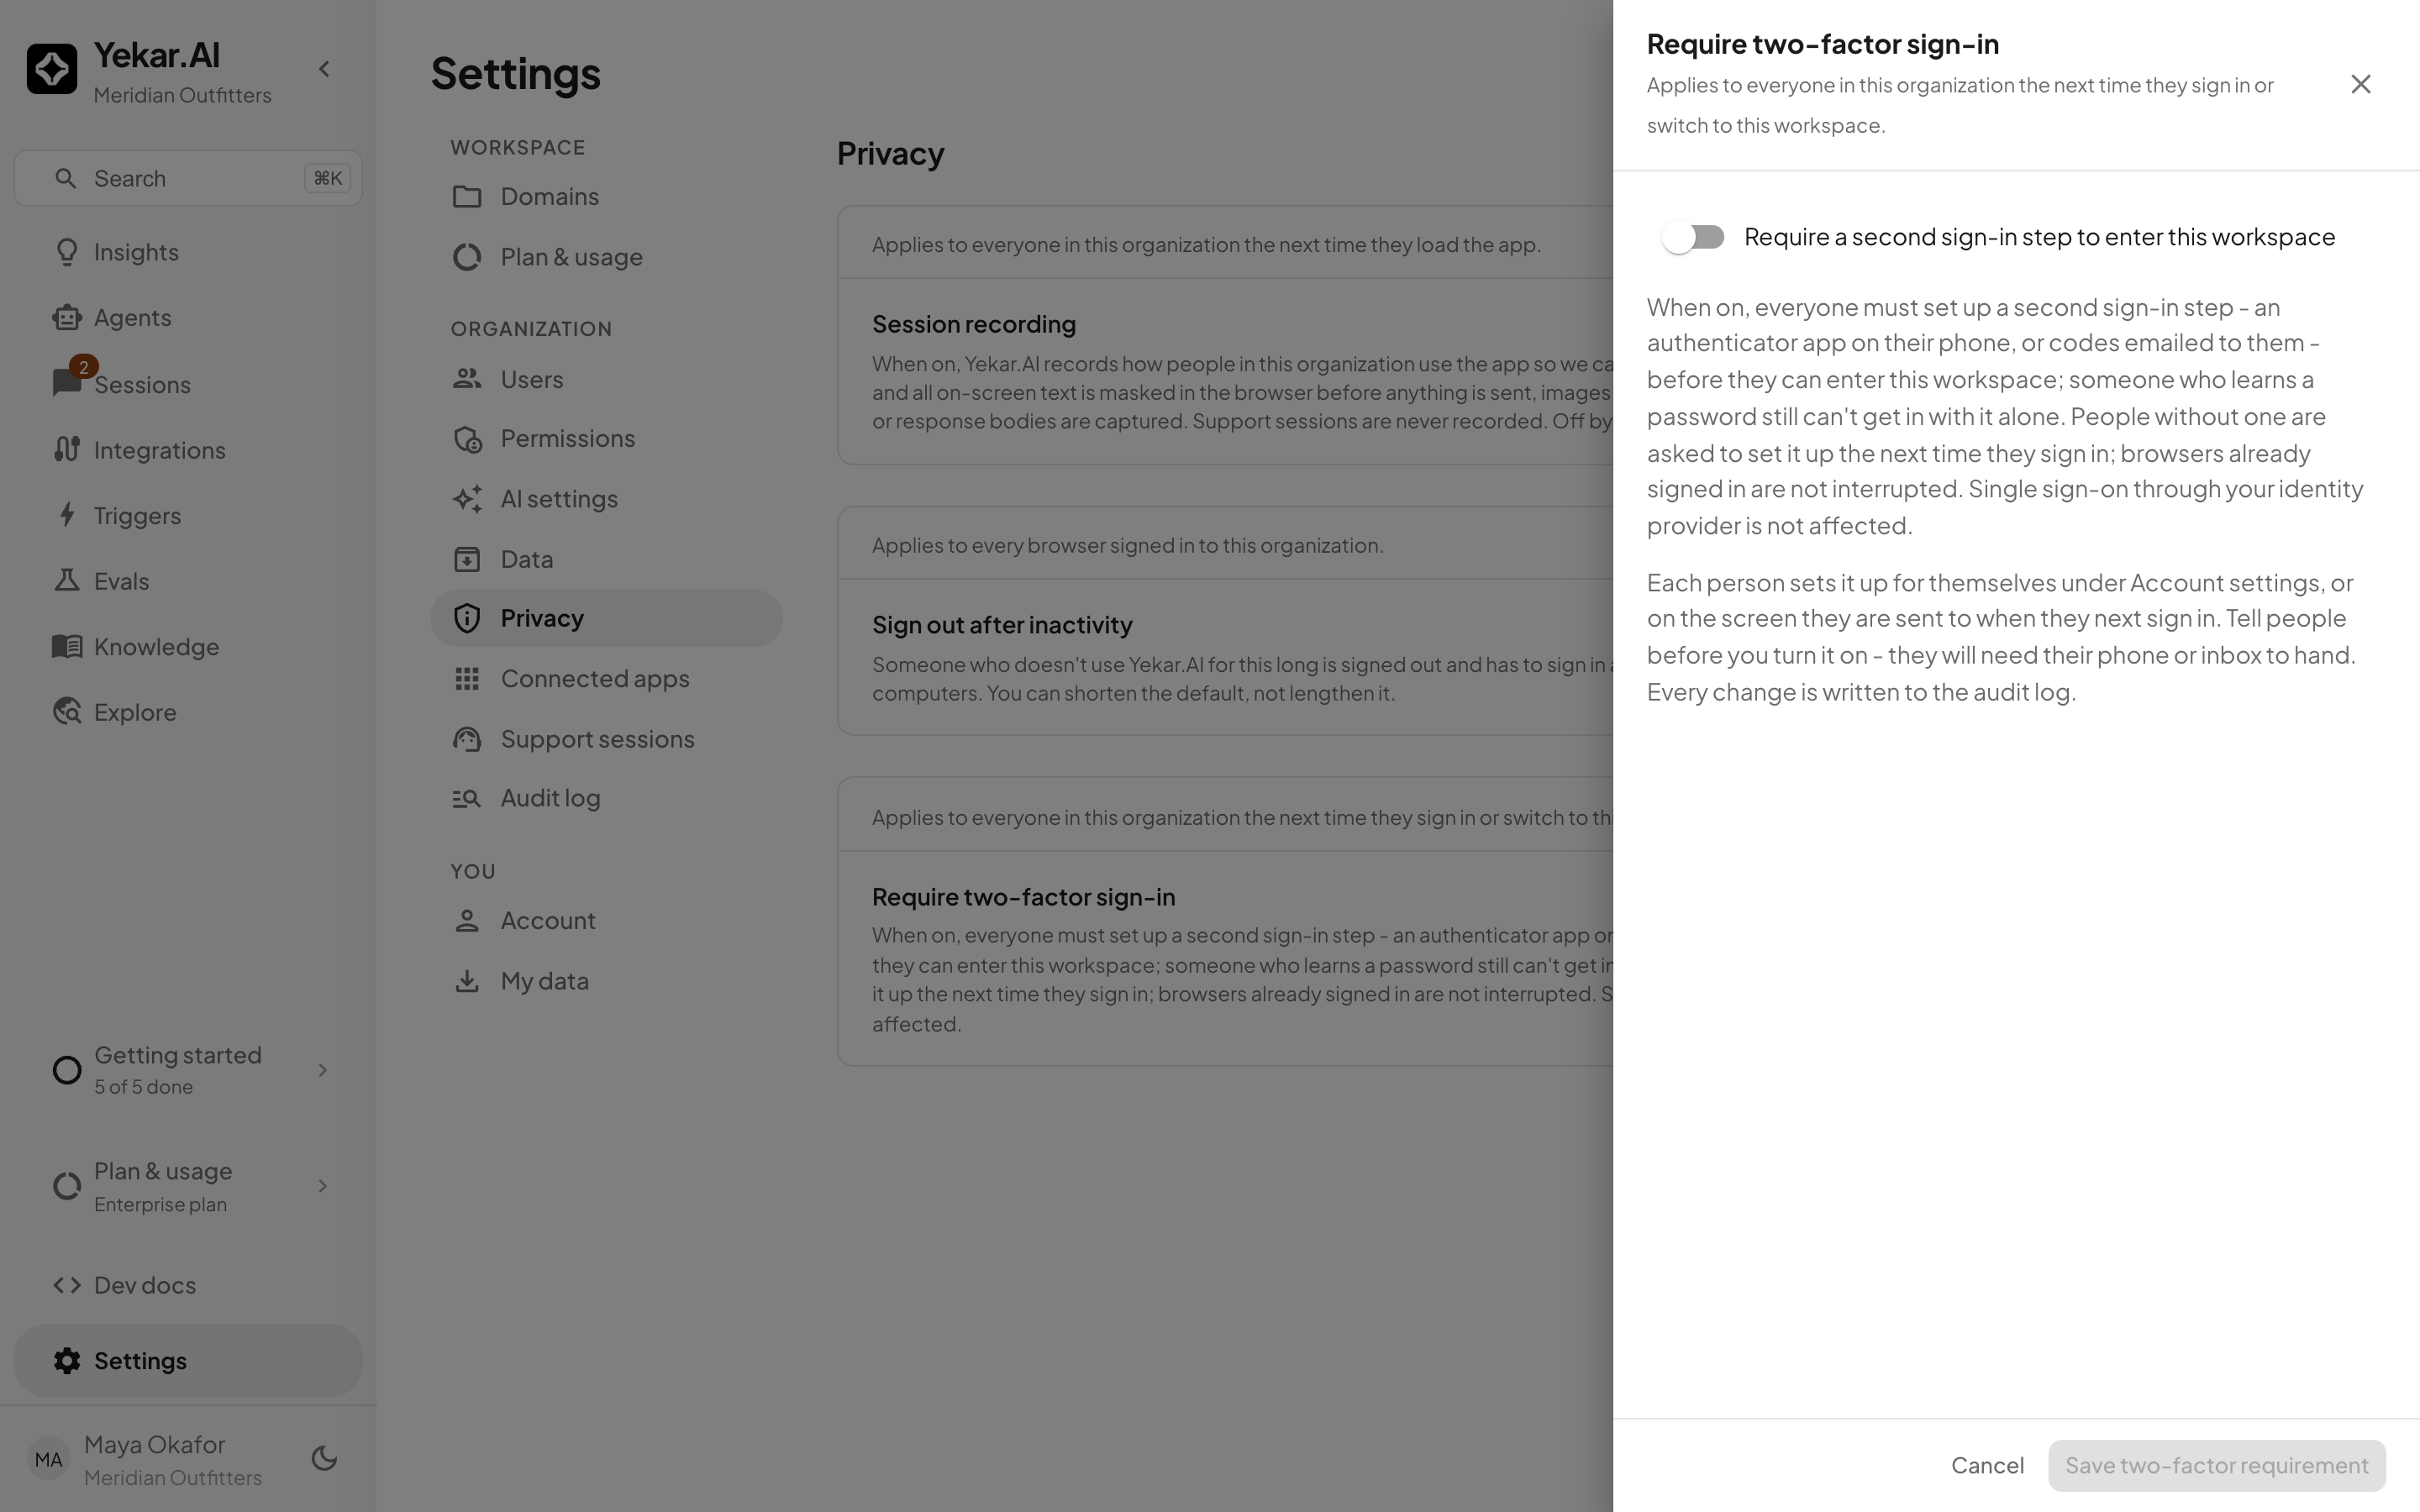
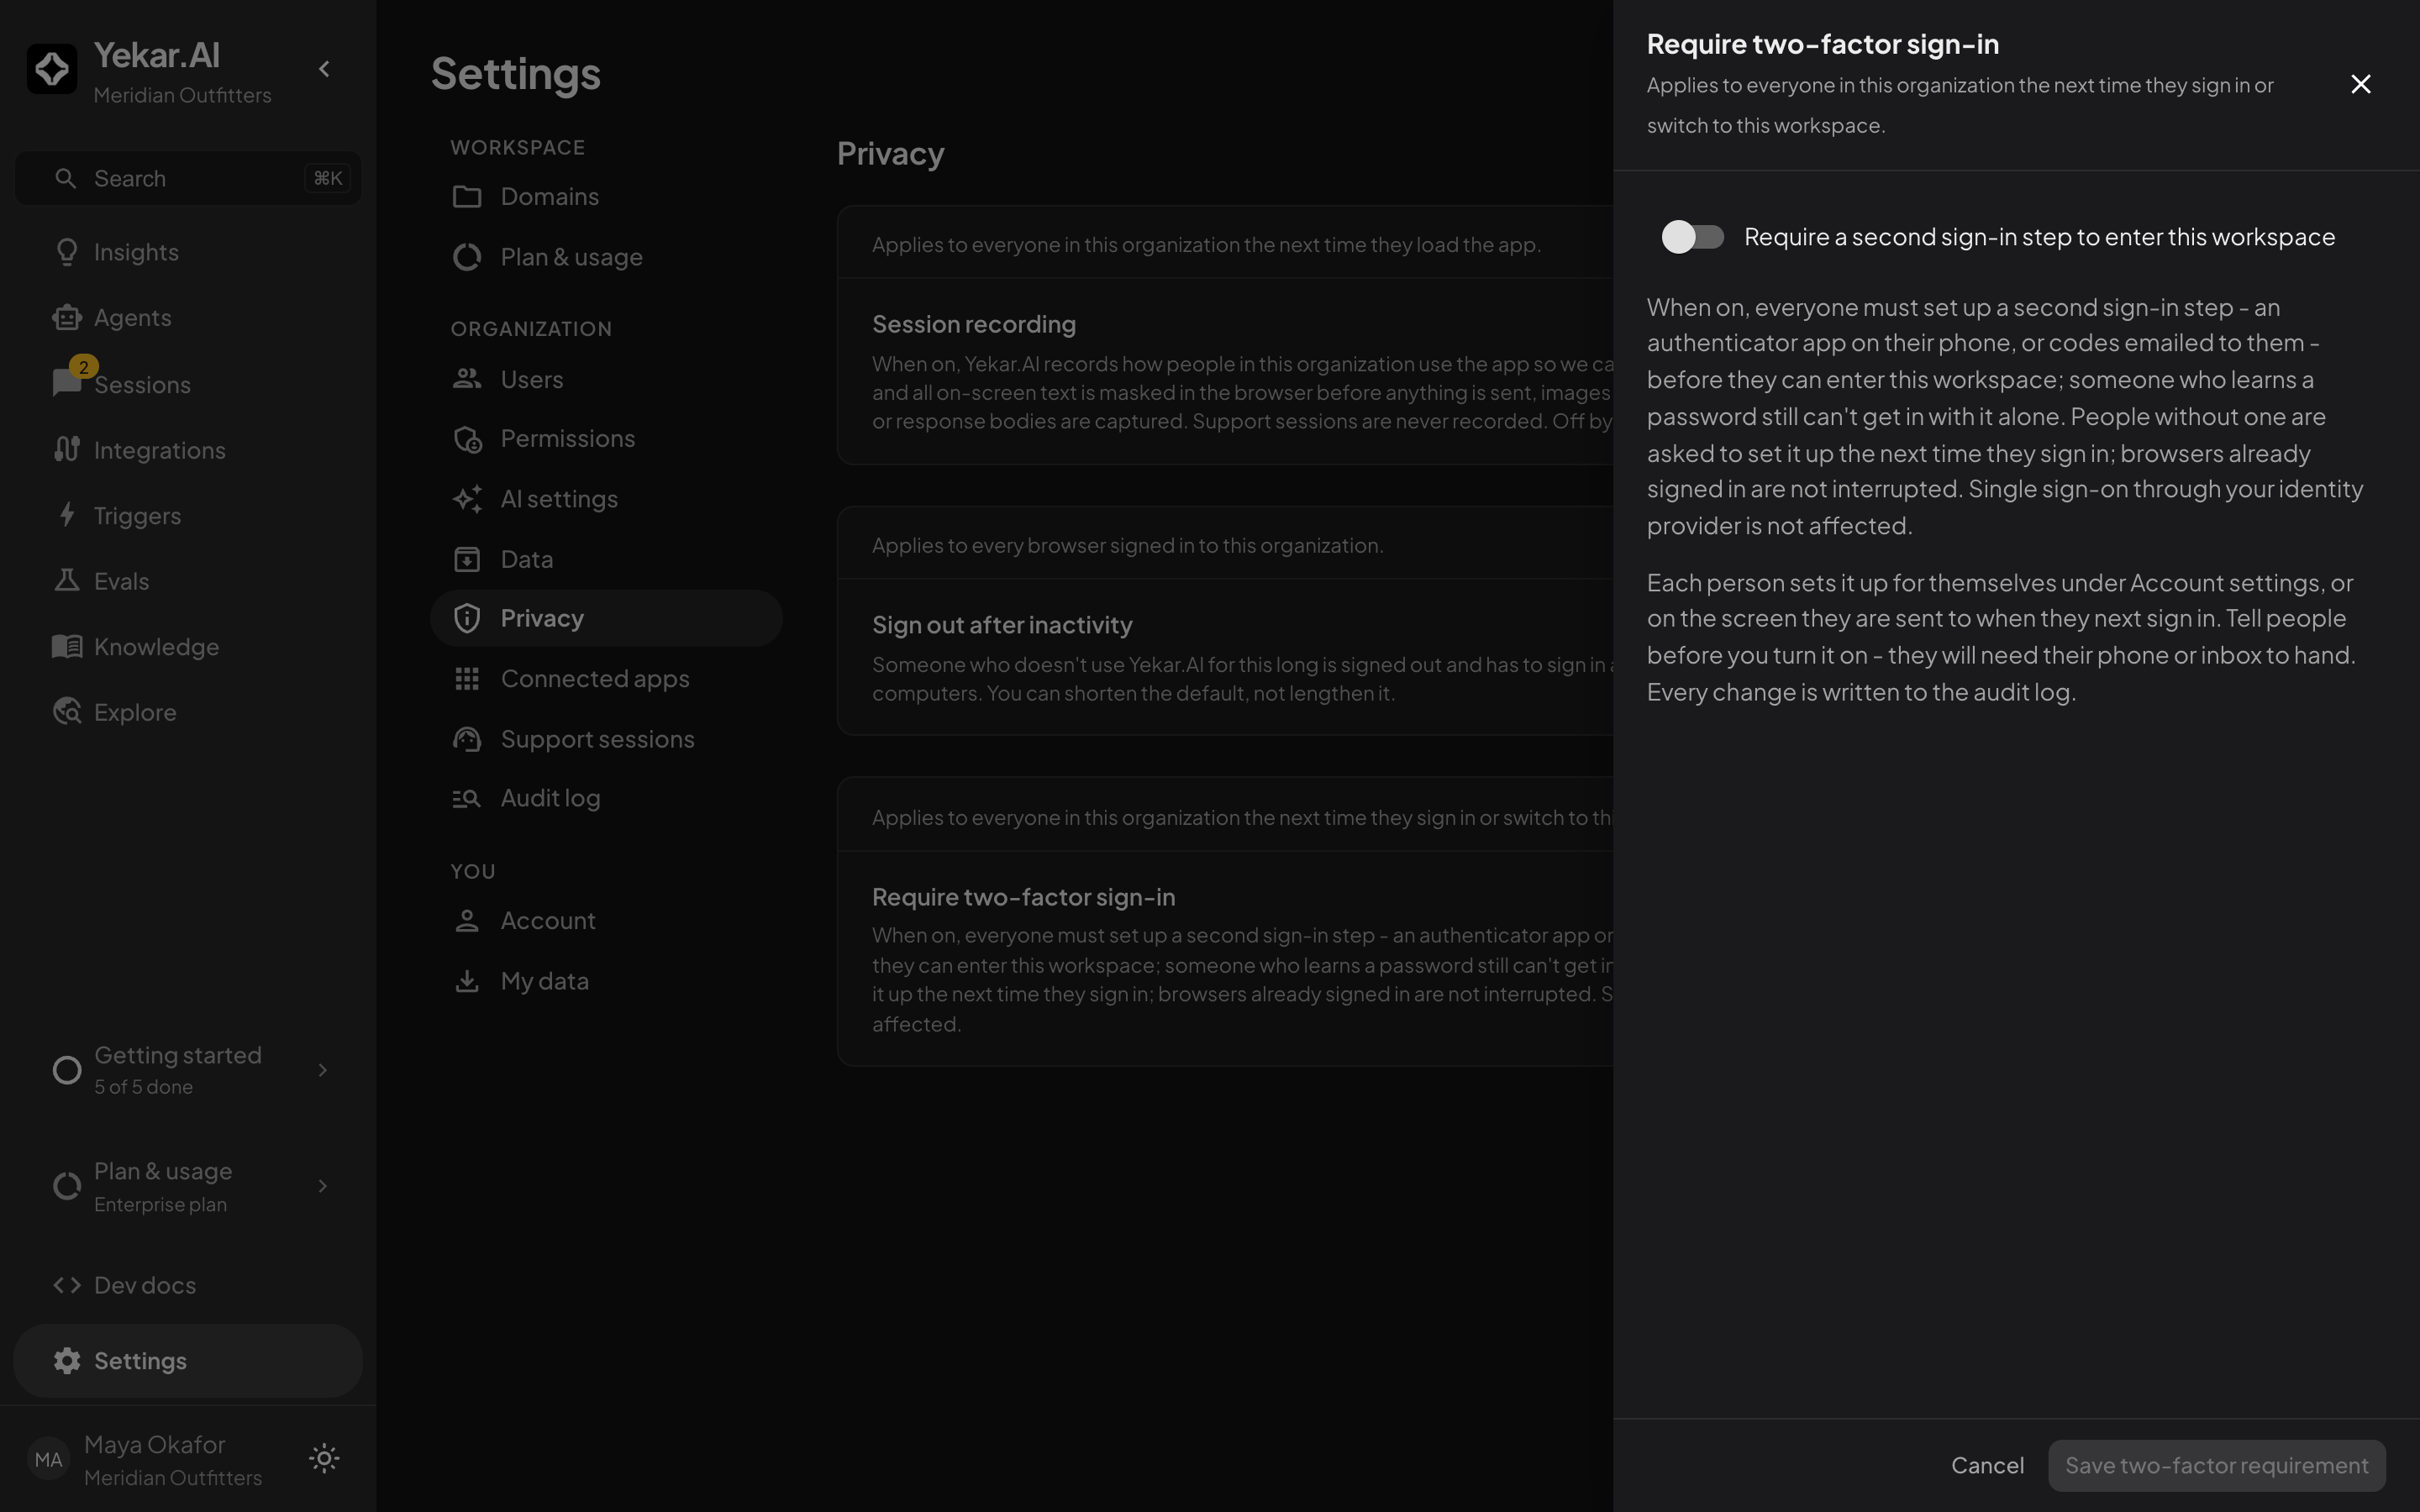
Require two-factor sign-in
Settings → Privacy → Require two-factor sign-in decides whether everyone in your organization must have a second sign-in step - an authenticator app, or codes emailed to them - before they can enter the workspace. It is off unless an organization Owner or Admin turns it on, and every change is written to the organization audit log. When you turn it on you also choose what counts as a second step:
- An authenticator app or emailed codes. People choose for themselves. Emailed codes need no app, but someone who controls a person's inbox could also reset their password through it.
- An authenticator app only. The stronger choice. People who use emailed codes are asked to switch to an app the next time they sign in: they confirm with one last emailed code, then scan the app's code.
When it is on, a person who has not set one up is still signed in to their account but not into this workspace: they are taken to a setup screen, and once they have confirmed their authenticator or emailed code and saved their recovery codes the workspace opens. People who already have one simply enter their code at sign-in as usual. It applies the next time each person signs in or switches to the workspace; browsers already signed in are not interrupted. Single sign-on through your identity provider is not affected - that provider decides its own second factor.
Each person sets up and manages their own second step under Settings → Account → Two-factor sign-in; see Team.
Error reports
When the app hits an unexpected error it may send a report so the fault can be fixed. Email addresses, access tokens and the query strings of web addresses are removed from the report before it leaves the browser, and it carries no IP address, cookies or account details. Error reports are not affected by the analytics choice above.
The website and documentation
yekar.ai and this documentation ask separately, with Cookie settings at the foot of every page. Google Analytics loads only after you accept; a cookieless page-view counter from our hosting provider runs either way. The cookie policy lists every cookie and what it is for.